EVO Wallet
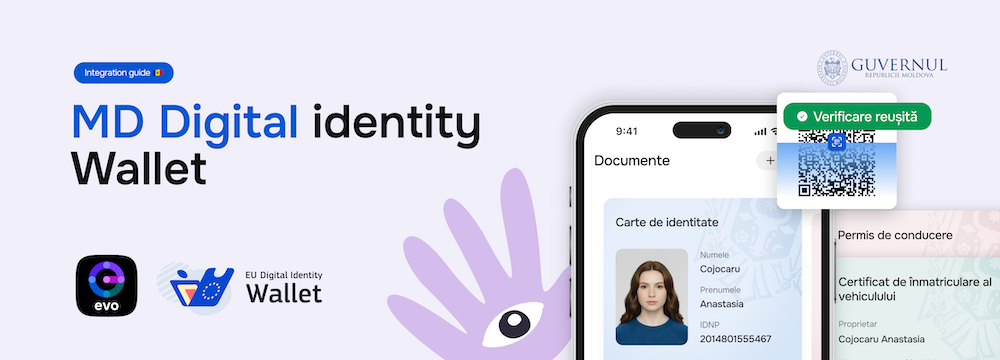
Following the EUDI Wallet regulation and its implementing acts, EVO Wallet implements remote presentation of attributes to wallet-relying parties according to OpenID4VP 1.0, using the mdoc format defined in ISO/IEC 18013-5, via same-device flow to retrieve documents. The mechanism is described in Section 8.3.1 of OpenID4VP 1.0 as direct_post.jwt response mode. Actual implementation profile is guided by OpenID4VC HAIP 1.0 with ISO mdoc as credential format.
OpenID4VP is an extension of OAuth 2.0 that enables the Holder (mdoc holder) to present Credential (mdoc) using its Wallet (mdoc app) to a Verifier (mdoc reader) upon request. In this context, the Wallet acts as OAuth 2.0 Authorization Server and the Verifier acts as OAuth 2.0 Client.
At a glance
What it is. The digital identity wallet inside the EVO government application. The citizen keeps the digital versions of their documents on the phone and presents them, on request, to a verifier — a bank, a counter, an online service — disclosing only the requested data and only with explicit consent. A system that needs to confirm a user's identity or specific attributes becomes a verifier (relying party) in the ecosystem, upon application to EGA. The implementation follows the European standards for the digital identity wallet.
Legal basis. HG nr. 5/2024 (aplicația guvernamentală integrată EVO), pct. 3 — desemnarea posesorului și deținătorului; HG nr. 677/2025 (consolidarea accesului în cadrul Portalului guvernamental integrat EVO). Temeiul specific al portofelului de identitate digitală — DE CONFIRMAT — HG nr. 5/2024, pct. 3.
Related acts: Legea nr. 91/2014; cadrul european privind identitatea digitală (eIDAS 2 / EUDI Wallet); standardele OpenID4VP 1.0 și ISO/IEC 18013-5 utilizate în implementare.
Who is accountable.
| Role | Entity |
|---|---|
| Holder | eGov Moldova (pentru EVO, conform HG nr. 5/2024) |
| Keeper | eGov Moldova |
| Technical operator (operator tehnico-tehnologic) | STISC |
Roles in an integration.
- eGov Moldova — holder/keeper of the platform; signs the integration agreement and registers the integrating system.
- STISC — issues the system certificate required for staging and production; operates the hosting infrastructure.
- Holder of the integrating system — decides the purpose and legal basis of use, the access rights, and is accountable for compliance.
- Development/integration team — implements and tests the technical integration.
- End user — the natural person or legal entity benefiting from the service.
Access conditions.
Gratuit. Calitatea de verificator se obține în baza cererii depuse la eGov Moldova, prin formularul dedicat, urmată de înregistrarea în ecosistem.
Who this guide is for.
Primary: development and integration teams of the holders of information systems, public and private. Secondary: project managers and compliance officers preparing the agreement with EGA and the STISC certificate.
Become a Verifier in the EVO Wallet Ecosystem ↗
Relying Parties in Production
Live Relying parties that have completed onboarding and accept EVO Wallet presentations in production.
Jump right in
Referenced standards
| Standard | Description |
|---|---|
| OpenID4VP 1.0 | OpenID for Verifiable Presentations 1.0 |
| OpenID4VC HAIP 1.0 | OpenID for Verifiable Credentials High Assurance Interoperability Profile 1.0 |
| RFC 6749 | The OAuth 2.0 Authorization Framework |
| RFC 8414 | OAuth 2.0 Authorization Server Metadata |
| RFC 9101 | The OAuth 2.0 Authorization Framework: JWT-Secured Authorization Request (JAR) |
| ISO/IEC 18013-5:2021 | Personal identification — ISO-compliant driving licence Part 5: Mobile driving licence (mDL) application |
| ISO/IEC TS 18013-7:2025 | Personal identification — ISO-compliant driving licence Part 7: Mobile driving licence (mDL) add-on functions |
| RFC 7049 | Concise Binary Object Representation (CBOR) |
| RFC 8152 | CBOR Object Signing and Encryption (COSE) |
| RFC 8610 | Concise Data Definition Language (CDDL): A Notational Convention to Express Concise Binary Object Representation (CBOR) and JSON Data Structures |
| RFC 9360 | CBOR Object Signing and Encryption (COSE): Header Parameters for Carrying and Referencing X.509 Certificates |
| IETF TSL draft | IETF Token Status List - draft-ietf-oauth-status-list-21 |